Find Out How Your Organization Responds to a Real Phishing Attack, Before an Attacker Does
Email is still the easiest way into most organizations. A convincing message, one rushed click and a stolen password can be enough to start a breach, regardless of how strong your firewall or endpoint protection is. Our Phishing Assessment tests that exposure in a safe and controlled way, using the same techniques real attackers use against your employees, executives and email defenses.
What Is a Phishing Assessment?
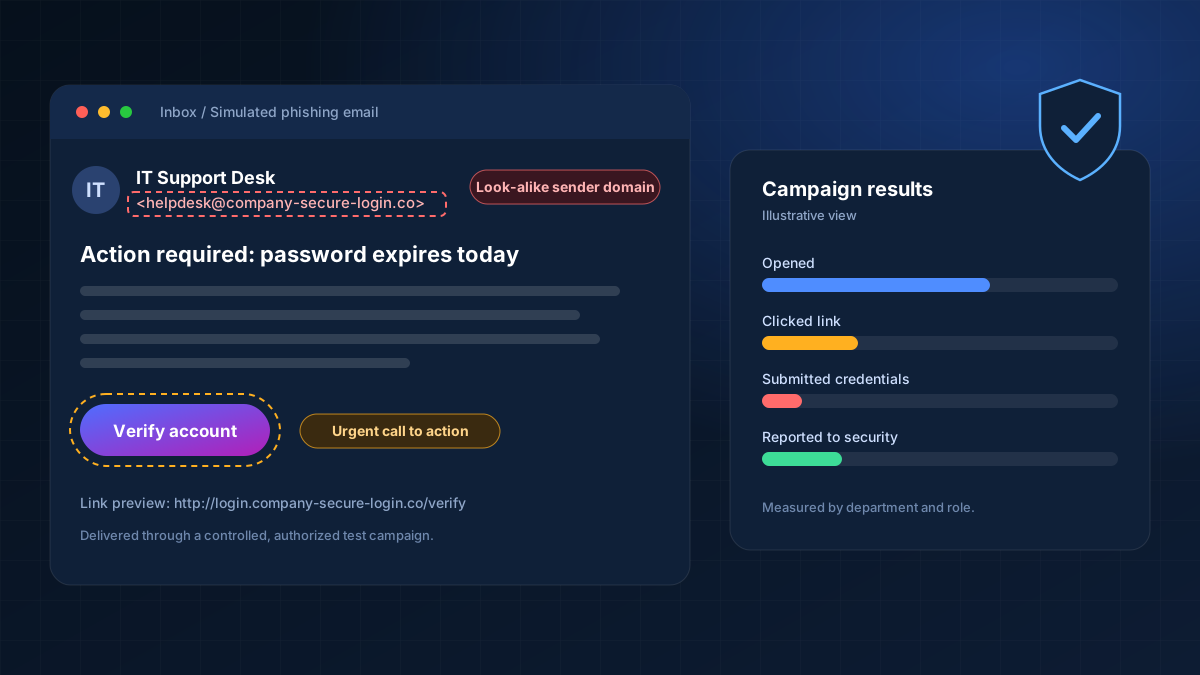
A phishing assessment is an authorized simulation of email-based social engineering attacks against your company. We design realistic campaigns, send them to the employees you approve, and measure what happens at every stage: who opens, who clicks, who enters credentials and, just as importantly, who reports the message. The result is a clear, evidence-based picture of your human risk and of how well your technical controls and incident response hold up.
What We Simulate
Bulk phishing campaigns
Brand-themed and business-themed emails sent across departments to measure overall susceptibility.
Spear phishing
Targeted messages built for executives, finance, HR and IT teams using publicly available information.
Credential harvesting
Look-alike login pages that test whether staff enter credentials, without storing any real passwords.
Attachment and link lures
Harmless, trackable documents and links that show who opens what they should not.
How the Assessment Works
- Scoping and written authorization We agree on target groups, scenarios, timing and rules of engagement, and record them in writing before anything is sent.
- Reconnaissance We gather publicly available information about your organization, as an attacker would, to make the scenarios realistic.
- Campaign design and setup We build the emails, landing pages and sending infrastructure, and confirm delivery with your team.
- Live campaign Messages go out and we track opens, clicks, submissions and reports in real time, escalating immediately if anything needs attention.
- Analysis and reporting We turn the results into findings by department and role, and review how your email security controls behaved.
- Debrief and remediation We walk your leadership and security team through the results and agree on practical next steps.
What You Receive
- An executive summary that explains your phishing risk in plain business terms.
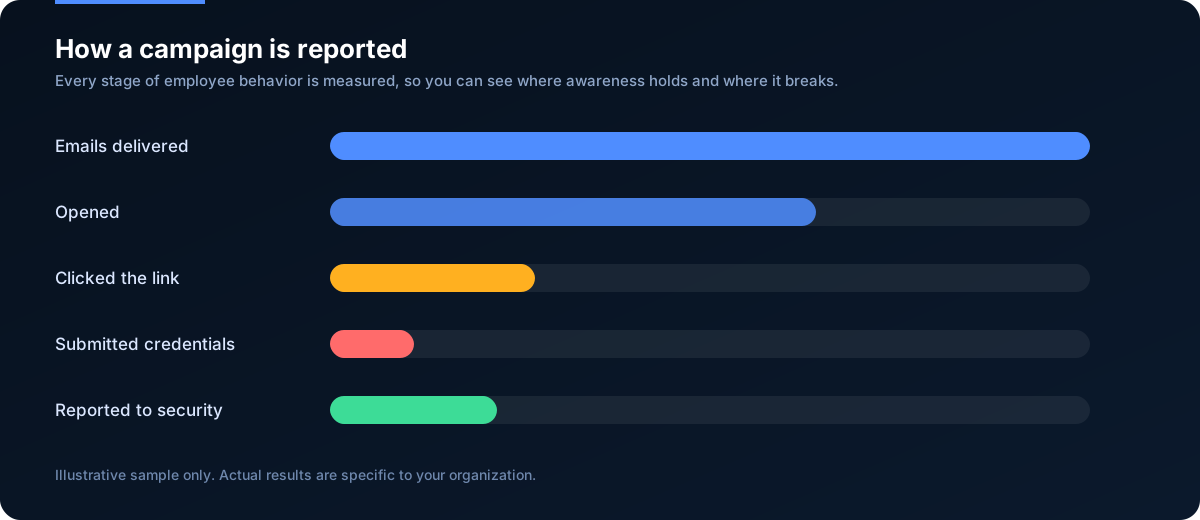
- Open, click, submission and reporting rates, broken down by department and role.
- A review of email security controls, including filtering, sender authentication (SPF, DKIM and DMARC) and reporting workflows.
- Evidence of what employees saw and did, for use in awareness sessions.
- A prioritized remediation roadmap covering people, process and technology.
- An optional retest to show measurable improvement over time.
Safe, Authorized and Confidential
Every engagement runs under written authorization and agreed rules of engagement. We use no real malware, we do not retain captured passwords, and results are shared only with the people you nominate. The goal is to help your employees learn, not to embarrass them.
Regular assessments also give you documented evidence of security awareness efforts, which can support audits and certifications such as ISO 27001 and SOC 2, and help show reasonable safeguards under data protection requirements like DPDP and GDPR.